GUIDESEPISODES
Old Next.js? Check your version and patch it
On October 14, 2026, Next.js shipped fixes for two critical holes and one high one. In some apps, a stranger could run their own code on your server. Your AI installed the version it remembered, and nobody updated it since. Here is how to read your label, get the recall list and patch it, in four steps checked against the Next.js, npm and GitHub docs.
01WHAT HAPPENED
Your app is on a recall list
Why it mattersYour AI installs the version it remembers. Security fixes after its training date never reach your app on their own.
Here’s the story. You built your app with an AI agent. It ran npm install next, picked the version it remembered, and the app shipped. Nobody touched that version again.
Open the full chapterIncludes a table, a note
Your AI’s memory has a date on it, like milk. It learned about Next.js up to a certain month. Security fixes that came out after that, it simply doesn’t know.
The October 14, 2026 security update
On October 14, 2026, the Next.js team published a security update: “Updates are now available in v16.4.1 (Active LTS) and v15.5.28 (Maintenance LTS) to address these issues. Please patch your Next.js dependencies to maintain the security of your applications.” They had announced it in advance on October 8.
| Advisory | Severity | Who is affected (Next.js’s words) |
|---|---|---|
Remote code execution in use cache functions returning typed arrays (GHSA-673q-mjm6-r5xr) | Critical | Apps “using App Router with Cache Components”. “There is no known workaround.” |
| Remote code execution in the Image Optimization API when using SVG (CVE-2026-96889) | Critical | When “Next.js runs on glibc-based Linux”. Workaround: sharp 0.35.5 or later |
| Denial of service in App Router using Server Actions (GHSA-p3m5-59mp-jv5r) | High | App Router with Server Actions. “Pages Router or not using Server Actions are not vulnerable.” |
Remote code execution means a stranger could run their own code on your server. Not every app is affected: it depends on your version and the features you use. But you don’t need to work that out. The Next.js team says to “upgrade immediately even if your application does not have similar functions.”
02STEP 1 · READ THE LABEL
Find the version you really run
Why it mattersYou can’t patch a version you haven’t read. One command, one line.
Open a terminal in your project folder and run one command. npm’s docs: it will “print to stdout all the versions of packages that are installed”.
Open the full chapterIncludes code, a note
# In your project folder:
npm ls next

# Example output (yours shows your own app name and version):
my-app@0.1.0 /Users/you/my-app
└── next@15.5.9
The line with next@ is the version your app really runs.
Why not just read package.json?
package.json usually holds a range, not a version. The ^ means “this version or any newer 15.x”:
{
  "dependencies": {
    "next": "^15.5.9"
  }
}
This says “15.5.9 or newer within 15”. It doesn’t say what is installed.
The exact version lives in package-lock.json, and your host installs from it. So npm ls next is the honest answer. Ask for npm ls next react react-dom to see React too.
03STEP 2 · GET THE RECALL LIST
npm audit lists every known hole
Why it mattersThe recall list tells you which jars to pull and which version replaces them.
The store keeps a recall list. So does npm. Its docs: “The audit command submits a description of the dependencies configured in your project to your default registry and asks for a report of known vulnerabilities.”
Open the full chapterIncludes code, a note
npm audit

# Only show High and Critical:
npm audit --audit-level=high
npm audit needs a package-lock.json. Each item shows the package, how bad it is, and the version that fixes it.
How to read it
- Start with Critical and High. Those are the holes worth fixing today.
- Note whether the package is one you installed yourself (in
package.json) or one that came along with another package. - Look for the fixed version. For
next, it should point you to the October 14 patches. - Some items are in tools you only use while building. Fix them too, but the ones your live app runs come first.
04STEP 3 · PATCH IT
Install the fixed version, on purpose
Why it mattersSame major version, small update, no surprises. A forced jump is how a security fix turns into a broken app.
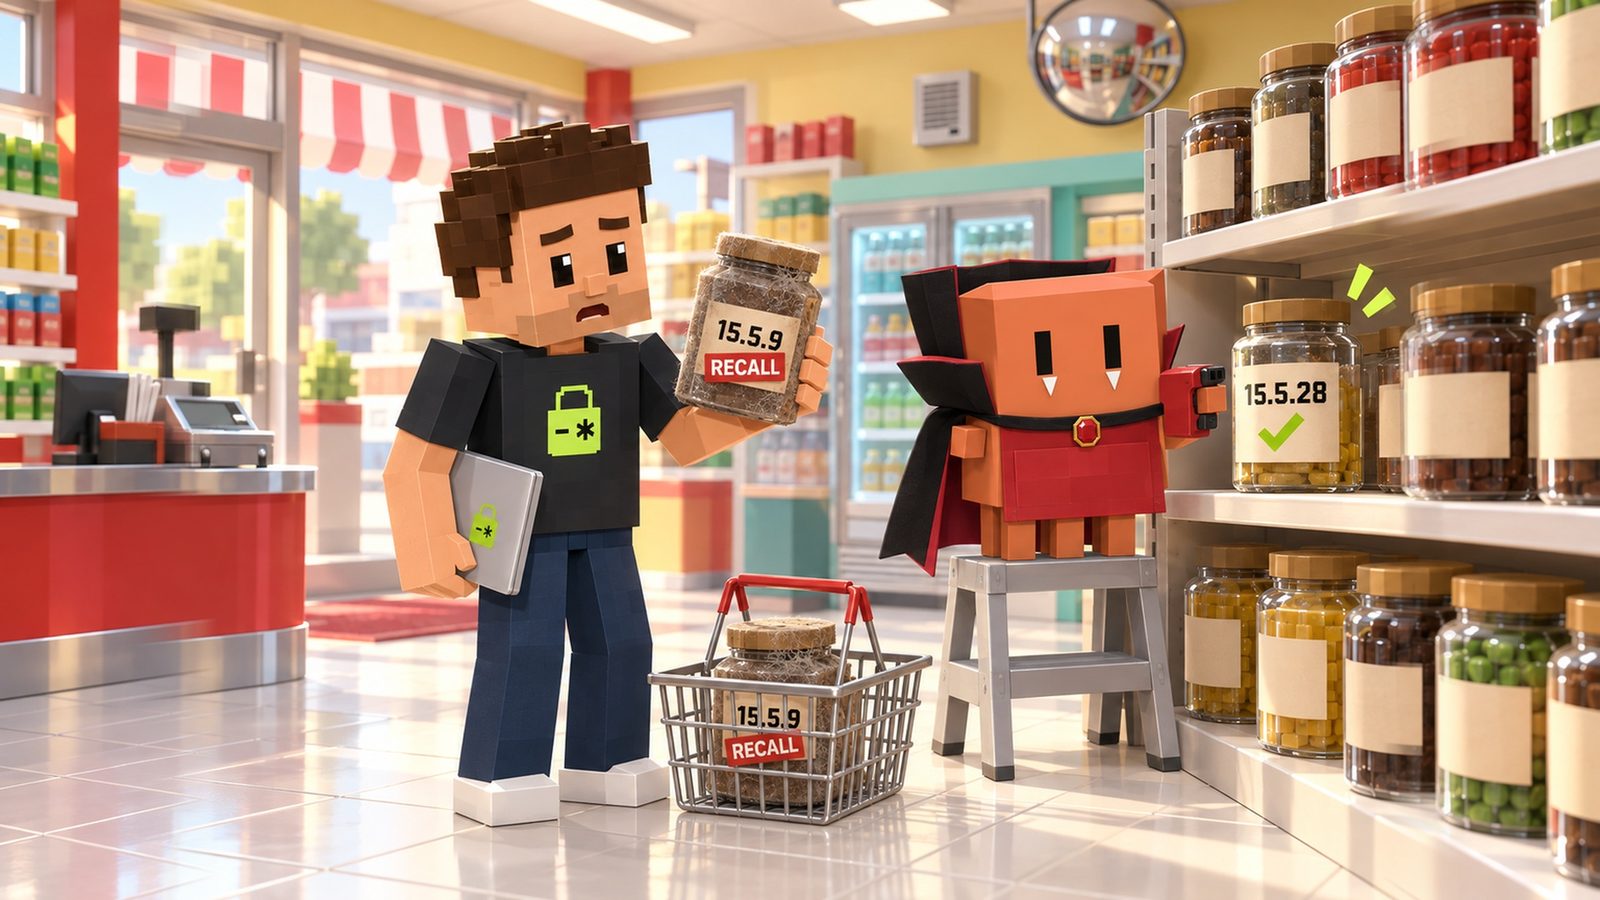
These are the exact commands from the Next.js security update. Pick the line for the major version you saw in step 1:
Open the full chapterIncludes code, a table, a note
# Your app is on Next.js 15:
npm install next@15.5.28

# Your app is on Next.js 16:
npm install next@16.4.1
Inside one major version, this is a small, normal update. Your app keeps the same features.
Your version, and what to install
npm ls next says | What to install | How big a change |
|---|---|---|
| 16.x, below 16.4.1 | npm install next@16.4.1 (or later) | Small: same major version |
| 15.x, below 15.5.28 | npm install next@15.5.28 (or later) | Small: same major version |
| 15.5.28 or newer, 16.4.1 or newer | Nothing for these fixes | Still run npm audit for other packages |
| 14.x or older | The October 14 post lists patches for 15.5 and 16.4 only | A major upgrade: plan it, test it, don’t rush it blind |
If npm audit also flags react or react-dom, upgrade them in the same commit. Two of the October advisories have related React advisories.
05STEP 3 · SHIP THE PATCH
Commit the lock file, redeploy, check again
Why it mattersA patch only counts once the live site runs it.
The patch exists on your laptop now. Your live site still runs the old jar until you ship it.
Open the full chapterIncludes code, a note
npm ls next          # check the new label: next@15.5.28 or next@16.4.1
npm run build        # make sure the app still builds
git add package.json package-lock.json
git commit -m "Patch Next.js for the October 14, 2026 security update"
git push             # your host builds and redeploys from this commit
npm audit            # run the recall list again
Commit both files together. package-lock.json is what pins the new version for your host.
Why both files
npm install changes package.json and package-lock.json. If only package.json goes up, your host may still install what the old lock file says. Same app, same old jar.
Then check the live site
- Open your host’s dashboard and wait for the new deployment to finish.
- Open your site and click through the main pages: sign in, the page that saves data, anything with images.
- Run
npm auditonce more. Anything still on the list needs a reason: no fix yet, or a major upgrade you planned for later.
06STEP 4 · GET THE RECALL NOTICES
Turn on Dependabot alerts
Why it mattersThe next recall reaches you, not the other way round.
You won’t always hear about the next recall from a video. GitHub can watch your packages for you and tell you when one has a known hole.
Open the full chapterIncludes steps, a note
- Open your repository on GitHub and click Settings.
- In the sidebar, under “Security and quality”, click Advanced Security.
- Next to Dependabot alerts, click Enable.
Turn it on and, in GitHub’s words, “you will see any results displayed on GitHub within minutes.” Each alert names the package, the hole and the fixed version.
07RESTOCKED
The whole fix on one page
Why it mattersRead the label, get the recall list, patch on purpose, get the notices.
Keep this next to your terminal.
Open the full chapterIncludes a table, a note
| What you see | What it means | What to do |
|---|---|---|
npm ls next says 15.x below 15.5.28 | You run a version from before the October 14 fixes | npm install next@15.5.28 |
npm ls next says 16.x below 16.4.1 | Same, on Next.js 16 | npm install next@16.4.1 |
npm audit lists High or Critical items | Known holes in your packages | Patch each to its fixed version, on purpose |
| An item needs a major version jump | A bigger change that can break things | Plan it. Never npm audit fix --force blind |
Only package.json changed in the commit | The host may install the old version | Commit package-lock.json too |
| The patch is on your laptop only | The live site still runs the old version | Push and redeploy |
| Dependabot alerts are off | Nobody tells you about the next recall | Settings → Advanced Security → Enable |
Then paste the prompt from the top of this page into Claude Code. It reads your versions, runs the audit, patches Next.js on purpose, and shows you the output before and after.
THE QUICK READ
What to take away.
In one minute.
- 01
On October 14, 2026, Next.js shipped fixes for two Critical holes and one High one. The patched versions are 15.5.28 and 16.4.1.
- 02
In some apps, a stranger could run their own code on your server. Next.js: “You should upgrade immediately even if your application does not have similar functions.”
- 03
npm ls nextprints the version you really run.package.jsononly shows a range; the lock file decides. - 04
npm auditis the recall list: it asks the registry “for a report of known vulnerabilities” in your packages. - 05
Don’t run
npm audit fix --forceblind. npm says it may install versions “outside your stated dependency range (including SemVer-major changes)”. - 06
A patch only counts once it’s live: commit
package.jsonandpackage-lock.jsontogether, redeploy, runnpm auditagain. - 07
Turn on Dependabot alerts in GitHub. The next recall reaches you without a video.
THE WHOLE RECALL, IN ONE PASTE
Paste this. Find every recalled package, then patch it.
Paste this into Claude Code, Cursor or any coding agent. It reports your versions and the audit first, never runs audit fix --force, and stops before any major version jump. Then it upgrades and commits package.json and package-lock.json. It never touches your .env values.
Check this project for packages with known security holes and patch them safely. Investigate before you change anything:
1. Run `npm ls next react react-dom` and tell me the exact installed versions.
2. Run `npm audit`. List every High and Critical item: the package, the installed version, the fixed version, and whether it is a direct dependency.
3. For Next.js: on 15.x upgrade to next@15.5.28 or later; on 16.x upgrade to next@16.4.1 or later (the October 14, 2026 security update). Upgrade react and react-dom too if npm audit flags them.
4. Do not run `npm audit fix --force`. If a fix needs a major version jump, stop and tell me what would change.
5. Commit package.json and package-lock.json together, run the build and the tests, and show me the output.
6. Run `npm audit` again and show me what is left, with a reason for anything you could not patch.
Never print or edit the values in my .env files.
Paste it into the agent you already build with
- Claude
- ChatGPT
- Gemini
- Cursor
- Copilot
QUESTIONS PEOPLE ASK
Good questions.
Short answers.
How do I check which Next.js version my app uses?
Run npm ls next in your project folder. It prints the version that is really installed. package.json usually shows a range like ^15.5.9, so it can’t tell you the exact version on its own.
What was the October 14, 2026 Next.js security update?
Fixes for three holes. Two are Critical: a stranger could run code through use cache functions or the Image Optimization API with SVG. One is High: a denial of service with Server Actions. The patched versions are 15.5.28 and 16.4.1.
Am I affected if I host on Vercel or Netlify?
The Next.js post doesn’t say any host makes you safe from these. It says “Please patch your Next.js dependencies.” Netlify’s changelog says apps on Netlify that meet the conditions are affected, and recommends upgrading and redeploying. Your app runs the version in your lock file, wherever it’s hosted.
What does npm audit fix --force do?
It lets npm install versions “outside your stated dependency range (including SemVer-major changes)”, in npm’s own words. That can move you to a new major version and break your app. Install the fixed version you chose instead, and plan any major upgrade.
Does updating Next.js break my app?
Moving within the same major version (15.x to 15.5.28, or 16.x to 16.4.1) is a small update. Still run npm run build and click through your main pages before you ship. A jump to a new major version is a bigger change: plan it and test it.
I use the Pages Router. Do I still need to update?
The Server Actions hole doesn’t affect “Applications using Pages Router or not using Server Actions”. The image hole depends on how Next.js runs, not on the router. The Next.js team says to upgrade either way.
What are Dependabot alerts?
A free GitHub feature that watches your packages and tells you when one has a known hole and which version fixes it. Turn it on in Settings → Advanced Security → Dependabot alerts → Enable. An alert tells you; you still patch.
Does Aster update my packages?
No. Aster reads your GitHub repository and flags vulnerable Next.js and package versions, with the next step. It doesn’t install updates, open upgrade pull requests or turn on Dependabot for you.
Read the label, get the recall list, patch on purpose, get the notices. Before you ship, check what your app really runs: your first repository audit is free, and Aster flags vulnerable Next.js and package versions in your repo.
Source notebook9 links
- Next.js Blog: Next.js Security Update for Upstream Vulnerabilities (October 14, 2026)
- Next.js Blog: the advance notice of the October 2026 security update (October 8, 2026)
- GitHub Advisory GHSA-673q-mjm6-r5xr (use cache, Critical)
- GitHub Advisory GHSA-2464-fhr4-w9xw / CVE-2026-96889 (Image Optimization with SVG, Critical)
- GitHub Advisory GHSA-p3m5-59mp-jv5r (Server Actions denial of service, High)
- npm Docs: npm ls (print the installed versions)
- npm Docs: npm audit (known vulnerabilities, audit fix and --force)
- Netlify Changelog: Next.js and React security vulnerabilities (October 14, 2026)
- GitHub Docs: Configuring Dependabot alerts